대표어
권호기사보기
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
결과 내 검색
동의어 포함
목차
표제지=0,1,1
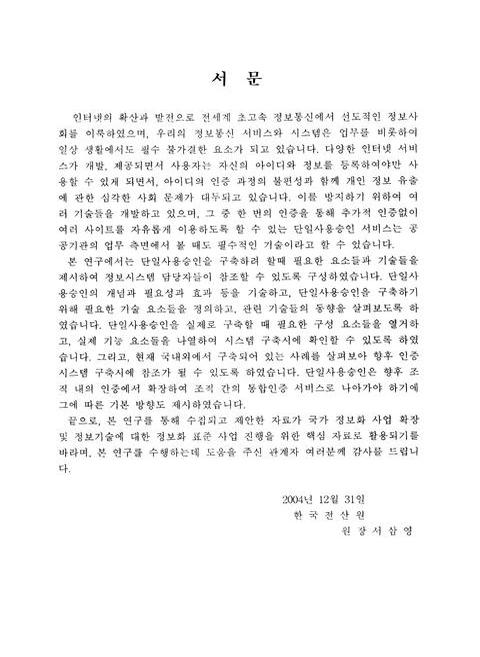
서문/서삼영=0,2,1
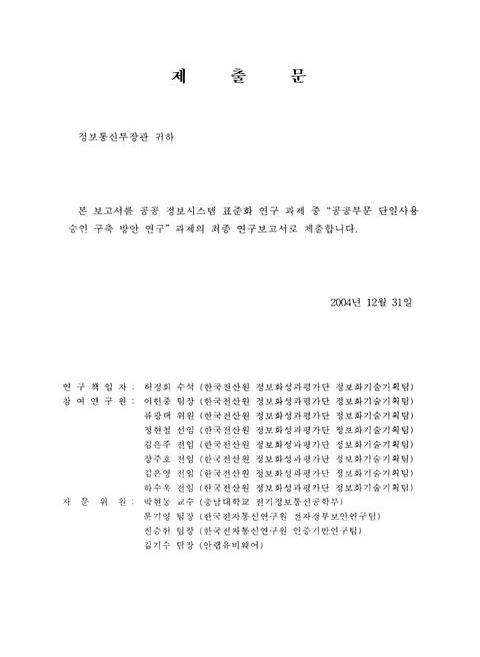
제출문=0,3,1
요약문=i,4,4
SUMMARY=v,8,1
CONTENTS=vi,9,4
FIGURES=x,13,2
TABLES=xii,15,1
목차=xiii,16,4
그림 목차=xvii,20,2
표 목차=xix,22,1
제1장 서론=1,23,2
제1절 작성의 목적=2,24,1
제2절 구성 및 적용대상=2,24,3
제2장 단일사용승인 개요=5,27,1
제1절 개념=5,27,2
제2절 필요성=6,28,2
1. 사용자 측면의 필요성=7,29,1
2. 조직 측면의 필요성=7,29,1
3. 관리자 측면의 필요성=8,30,1
제3절 주요기능 요건=8,30,4
제4절 기대효과=11,33,2
제3장 관련 기술 동향=13,35,1
제1절 인증 기술=13,35,2
1. ID/패스워드=14,36,1
가. 일반 패스워드 방식=14,36,3
나. 일회용 패스워드(one-time password) 방식=16,38,1
다. 패스워드 방식에 대한 고찰=17,39,1
2. 공개키 기반 구조(PKI:Public Key Infrastructure)=17,39,1
가. PKI 구성=17,39,3
나. 인증서 발급 시나리오=19,41,2
다. 공개키인증서 (Public Key Certificate)=21,43,2
3. 스마트카드=22,44,1
가. 스마트카드의 정의=22,44,1
나. 스마트카드의 종류=23,45,1
1) 접촉식(Contact) 카드=23,45,1
2) 비접촉식(Contactless) 카드=23,45,1
3) 콤비카드(Combi Card)=23,45,1
4) 하이브리드 카드(Hybrid Card)=24,46,1
다. 스마트카드의 응용=24,46,2
4. 생체인식=26,48,2
가. 지문인식=27,49,3
나. 홍채인식=29,51,3
다. 정맥인식=31,53,2
라. 안면인식=32,54,2
마. 생체정보의 스마트카드에 적용=33,55,2
제2절 보안 프로토콜=35,57,1
1. SSL/TLS=35,57,1
가. SSL의 구조=35,57,2
1) 세션 정보=36,58,1
2) 연결 정보=36,58,2
나. SSL에서 제공하는 보안 서비스=37,59,1
1) 두 응용간의 기밀성 서비스=38,60,1
2) 클라이언트와 서버의 상호 인증=38,60,1
3) 메시지 무결성 서비스=38,60,1
다. SSL과 TLS=38,60,1
2. 커버로스(Kerberos)=38,60,2
가. 커버로스 프로토콜 기본 개념=39,61,1
1) 키 배포=39,61,3
2) 세션 티켓=41,63,2
나. 커버로스 프로토콜 동작=42,64,1
1) AS Exchange=42,64,2
2) TGS Exchange=43,65,2
3) CS Exchange=44,66,2
3. SAML=46,68,3
제3절 인증 서비스 동향=49,71,1
1. .Net Passport=49,71,2
2. 리버티 얼라이언스(Liberty Alliance)=50,72,3
3. 3-D Secure=52,74,2
4. 시볼레(Shibboleth)=53,75,2
5. PingID Network=54,76,2
제4장 단일사용승인 기능요건 분석=56,78,1
제1절 보안성 확보 기능 요건=56,78,1
1. 단일 사용자 인증 기능 요건=57,79,3
2. 인증 정보 암호화 기능 요건=59,81,3
3. 인증 정보 무결성 확보 기능 요건=61,83,2
제2절 응용 서비스 시스템 연동 기능 요건=63,85,1
1. 응용 서비스 시스템 연동 유형 분류=63,85,1
2. 비패키지, 에이전트 적용 응용 연동 개념 및 기능 요건=64,86,1
가. 연동 개념=64,86,2
나. 연동 기능 요건=65,87,2
3. 비패키지, 에이전트 비적용 응용 연동 개념 및 기능 요건=66,88,1
가. 연동 개념=66,88,2
나. 연동 기능 요건=67,89,2
4. 패키지, 에이전트 적용 응용 연동 개념 및 기능 요건=68,90,1
가. 연동 개념=68,90,2
나. 연동 기능 요건=69,91,2
5. 패키지, 에이전트 비적용 응용 연동 개념 및 기능 요건=70,92,1
가. 연동 개념=70,92,2
나. 연동 기능 요건=72,94,1
6. 사용자 인증 정보 통합 기능 요건=72,94,2
제3절 관리 기능 요건=74,96,1
1. 무 중단 서비스 제공 기능 요건=74,96,1
2. 사용자 등록 관리 기능 요건=74,96,3
3. 로그 관리 기능 요건=76,98,2
4. 조직간 단일사용승인 연동 기능 요건=77,99,3
제5장 사례 연구=80,102,1
제1절 국내 사례=80,102,1
1. 공공기관 A:PKI 기반 SSO 구축 사례=80,102,1
가. 구축 배경=80,102,1
나. 구축 내용=80,102,3
다. 구축 효과=82,104,1
2. 공공기관 B 통합인증시스템 구축 사례=82,104,1
가. 구축 배경=82,104,2
나. 구축 내용=83,105,3
다. 구축 효과=85,107,2
3. 국내 기업 C:ID/패스워드 기반의 SSO 구축 사례=87,109,1
가. 구축 배경=87,109,2
나. 구축 내용=88,110,2
다. 구축 효과=89,111,1
제2절 국외 사례=90,112,1
1. 미국 정부의 e-Authentication 구축 사례=90,112,3
2. 일본 정부의 EduMart 사례=92,114,3
제6장 결론=95,117,4
판권지=99,121,1
영문목차
[title Page etc.]=0,1,8
CONTENTS=vi,9,14
Chapter 1. Introduction=1,23,2
Section 1. Purpose=2,24,1
Section 2. Composition and Application Target=2,24,3
Chapter 2. Single Sign On=5,27,1
Section 1. Concept=5,27,2
Section 2. Necessity=6,28,2
1. Necessity in User Part=7,29,1
2. Necessity in Organization Part=7,29,1
3. Necessity in Administrator Part=8,30,1
Section 3. Essential Functional Requirements=8,30,4
Section 4. Expected Effect=11,33,2
Chapter 3. Technology Trend=13,35,1
Section 1. Authentication Technology=13,35,2
1. ID/Password=14,36,1
A. General Password Method=14,36,3
B. One-Time password Method=16,38,1
C. Consideration for Password Method=17,39,1
2. Public Key Infrastructure=17,39,1
A. PKI Structure=17,39,3
B. Certificate issuing scenario=19,41,2
C. Public Key Certificate=21,43,2
3. Smartcard=22,44,1
A. Definition=22,44,1
B. Type=23,45,1
1) Contact Card=23,45,1
2) Contactless Card=23,45,1
3) Combi Card=23,45,1
4) Hybrid Card=24,46,1
C. Application=24,46,2
4. Biometrics=26,48,2
가. Finger-scan=27,49,3
나. Iris-scan=29,51,3
다. Vein-scan=31,53,2
라. Face-scan=32,54,2
마. Smart Card Application in Biometrics=33,55,2
Section 2. Security Protocol=35,57,1
1. SSL/TLS=35,57,1
A. SSL Structure=35,57,2
1) Session information=36,58,1
2) Connection information=36,58,2
B. Security Service by SSL=37,59,1
1) Confidentiality Service between two applications=38,60,1
2) Cross-Authentication between Client and Server=38,60,1
3) Message Integrity Service=38,60,1
C. SSL and TLS=38,60,1
2. Kerberos=38,60,2
A. Kerberos Protocol Basic Concept=39,61,1
1) Key Distribution=39,61,3
2) Session Ticket=41,63,2
B. Kerberos Protocol Operation=42,64,1
1) AS Exchange=42,64,2
2) TGS Exchange=43,65,2
3) CS Exchange=44,66,2
3. SAML=46,68,3
Section 3. Trend for Authentication Service=49,71,1
1. .Net Passport=49,71,2
2. Liberty Alliance=50,72,3
3. 3-D Secure=52,74,2
4. Shibboleth=53,75,2
5. PingID Network=54,76,2
Chapter 4. Single Sign On Functional Requirement=56,78,1
Section 1. Functional Requirements for Guaranteeing Security=56,78,1
1. One-user Certification Functional Requirement=57,79,3
2. Authentication Information encryption Functional Requirement=59,81,3
3. Guaranteed Integrity of Authentication Information Functional Requirement=61,83,2
Section 2. Application Service System Connection Functional Requirement=63,85,1
1. Application Service System Connection Type=63,85,1
2. Non-package, Agent Application Connection Type=64,86,1
가. Connection Concept=64,86,2
나. Functional Requirement for Connection=65,87,2
3. Non-package, Agent Non-application Connection Type=66,88,1
가. Connection Concept=66,88,2
나. Connection Functional Requirement=67,89,2
4. Package, Agent Application Connection Type=68,90,1
가. Connection Concept=68,90,2
나. Connection Functional Requirement=69,91,2
5. Package, Agent Non-application Connection Type=70,92,1
가. Connection Concept=70,92,2
나. Connection Functional Requirement=72,94,1
6. User Authentication Information Integrating Functional Requirement=72,94,2
Section 3. Functional Requirement for Management=74,96,1
1. Seamless Service Functional Requirement=74,96,1
2. User Registration Management Functional Requirement=74,96,3
3. Log Management Functional Requirement=76,98,2
4. Connection between organizations Functional Requirement=77,99,3
Chapter 5. Case study=80,102,1
Section 1. Domestic case=80,102,1
1. Public sector A:SSO based on PKI=80,102,1
가. Background=80,102,1
나. Implementation Details=80,102,3
다. Effect=82,104,1
2. Public sector B:Integrated SSO System=82,104,1
가. Background=82,104,2
나. Implementation Details=83,105,3
다. Effect=85,107,2
3. Company C:SS0 based on ID/Password=87,109,1
가. Background=87,109,2
나. Implementation Details=88,110,2
다. Effect=89,111,1
Section 2. Foreign case=90,112,1
1. US Govermment:e-Authentication=90,112,3
2. Japan Government:EduMart=92,114,3
Chapter 6. Conclusion=95,117,4
Copyright=99,121,1
[그림 2-3] 단일사용승인 개념=5,27,1
[그림 4-2] 단일사용승인 주요기능=8,30,1
[그림 2-5] 통합서버형 단일사용승인=9,31,1
[그림 2-6] ID 연계형 단일사용승인=10,32,1
[그림 3-1] 패스워드 인증 방법=15,37,1
[그림 3-2] One-time 패스워드 시스템=16,38,1
[그림 3-3] PKI 시스템의 구성=18,40,1
[그림 3-4] 인증서 발급 과정=20,42,1
[그림 3-5] 인증서 프로파일=22,44,1
[그림 3-6] 스마트카드의 응용분야=24,46,1
[그림 3-7] 생체인식의 종류=27,49,1
[그림 3-8] 지문 입력 장치 및 지문인식=28,50,1
[그림 3-9] 지문 인식 시스템도=29,51,1
[그림 3-10] 홍채인식 과정 구성도=31,53,1
[그림 3-11] 정맥인식 시스템도=32,54,1
[그림 3-12] 얼굴 인식 시스템의 얼굴 인식 순서=33,55,1
[그림 3-13] SSL 프로토콜 구조=35,57,1
[그림 3-14] 키 배포(이론상)=40,62,1
[그림 3-15] 키 배포(실제)=41,63,1
[그림 3-16] 상호 인증(클라이언트/서버)=42,64,1
[그림 3-17] AS Exchange=43,65,1
[그림 3-18] TGS Exchange=44,66,1
[그림 3-19] CS Exchange=45,67,1
[그림 3-20] SAML 도메인 모델=47,69,1
[그림 3-21] SAML 요소들=48,70,1
[그림 3-22] .Net Passport=50,72,1
[그림 3-23] Liberty Alliance=52,74,1
[그림 4-1] 단일사용승인 연동 개념도=63,85,1
[그림 4-2] 비패키지, 에이전트 적용 응용 연동 개념도=64,86,1
[그림 4-3] 비패키지, 에이전트 비적용 응용 연동 개념도=66,88,1
[그림 4-4] 패키지, 에이전트 적용 응용 연동 개념도=69,91,1
[그림 4-5] 패키지, 에이전트 비적용 응용 연동 개념도=71,93,1
[그림 4-6] 공공서비스를 위한 조직간의 단일사용승인 구축(예)=79,101,1
[그림 5-1] PKI 기반 SSO 구축 개념도=81,103,1
[그림 5-2] 통합인증시스템 구축 개념도=85,107,1
[그림 5-3] 통합 인증 시스템 구성도=89,111,1
[그림 5-4] e-Authentication 개념도=90,112,1
[그림 5-5] Outline of Edumart Verification Test=93,115,1
*표시는 필수 입력사항입니다.
| 전화번호 |
|---|
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
| 번호 | 발행일자 | 권호명 | 제본정보 | 자료실 | 원문 | 신청 페이지 |
|---|
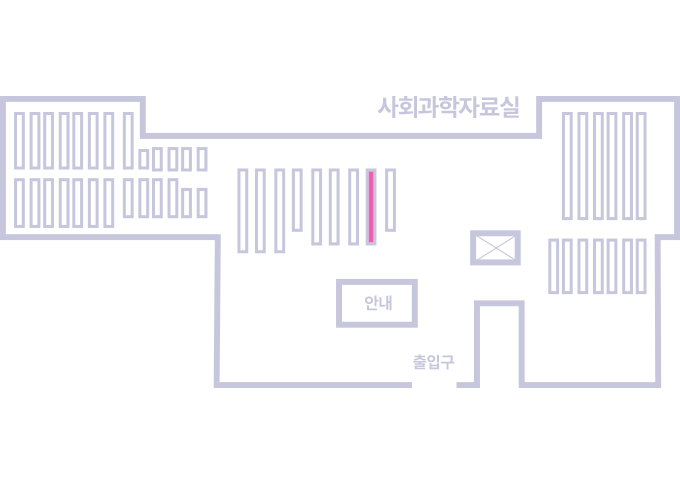
도서위치안내: / 서가번호:
우편복사 목록담기를 완료하였습니다.
*표시는 필수 입력사항입니다.
저장 되었습니다.