대표어
권호기사보기
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
결과 내 검색
동의어 포함
목차
표제지=0,1,1
인사말씀/한국전자통신연구원 원장 임주환=0,2,2
제출문=1,4,2
요약문=3,6,6
SUMMARY=9,12,6
CONTENTS=15,18,4
List of Figures=19,22,1
List of Tables=20,23,1
목차=21,24,4
그림 목차=25,28,1
표 목차=26,29,1
제1장 서론=27,30,3
제1절 연구의 필요성=29,32,2
제2절 연구의 목표 및 내용=31,34,1
1. 최종목표=31,34,1
2. 1차년도 (2002년) 목표 및 내용=32,35,1
3. 2차년도 (2003년) 목표 및 내용=33,36,1
4. 3차년도 (2004년) 목표 및 내용=34,37,1
제3절 연구의 결과 및 실적=35,38,1
1. 정보통신기술협회(TTA) 표준화 제정 현황=35,38,3
2. ECIF 표준화 제정 현황=37,40,3
3. ASTAP 표준화 제정 현황=40,43,3
4. 연구결과물=43,46,6
제4절 연구결과물 활용 분야 및 기대 효과=49,52,1
1. 활용 분야=49,52,1
2. 기대 효과=49,52,3
제5절 보고서 구성=51,54,2
제2장 XML 정보보호 기술 개요=53,56,4
제1절 XML 전자서명 기술=56,59,3
제2절 XML 암호 기술=59,62,3
제3절 XML 기반 키 관리 기술=61,64,4
제4절 XML 기반 접근제어 기술=64,67,5
제5절 XML 기반 보안 정보 교환 기술=68,71,5
제3장 XML 정보보호 기술 동향 연구=73,76,3
제1절 XML 정보보호 표준화 동향 연구=75,78,1
1. 표준화 단체 동향=75,78,7
2. 기술별 표준화 동향=81,84,5
제2절 XML 정보보호 시장 동향 연구=85,88,2
1. 세계 시장 동향=86,89,3
2. 국내 시장 동향=88,91,2
제3절 XML 정보보호 제품 동향 연구=89,92,6
제4장 XML 정보보호 기술 적용 분야 표준화 연구=95,98,3
제1절 XML 전자서명 표준 적합성 시험 방안 연구=97,100,2
1. XML 전자서명 표준적합성 시험 방안=98,101,6
2. XML 전자서명 표준적합성 시험 도구=103,106,4
3. 연구 확장 방안=107,110,3
제2절 UDDI 접근제어를 위한 XACML 적용방안=109,112,2
1. UDDI 기술 개요=110,113,5
2. UDDI와 XML 접근 제어 기술 연동=114,117,4
3. 국내 표준 적용 방안 연구=117,120,2
제3절 전자정부 보안 표준화 연구=118,121,1
1. 전자정부 개요=118,121,2
2. 전자정부 서비스를 위한 보안 요구사항=119,122,10
제5장 결론=129,132,4
부록=133,136,2
부록A. 참고문헌=135,138,6
부록B. 용어/약어 설명=141,144,2
부록C. 연구 결과물 목록=143,146,1
1. 총괄내역=143,146,1
2. 표준(안)=143,146,2
3. 특허=145,148,1
4. 논문=145,148,2
5. 프로그램=146,149,1
6. 기술문서=147,150,2
부록D. 표준 제정 내용 요약=149,152,15
영문목차
[title page etc.]=0,1,17
CONTENTS=15,18,12
Chapter1 Introduction=27,30,3
Section1. Necessity=29,32,2
Section2. Objectives and Contents of the Research=31,34,1
1. Ultimate goals=31,34,1
2. Purpose and scope of research in 1st(이미지참조) year (2002)=32,35,1
3. Purpose and scope of research in 2nd(이미지참조) year (2003)=33,36,1
4. Purpose and scope of research in 3nd(이미지참조) year (2004)=34,37,1
Section3. Results and Outcomes of the Research=35,38,1
1. Present state for establishment of TTA standardization=35,38,3
2. Present state for establishment of ECIF standardization=37,40,3
3. Present state for establishment of ASTAP standardization=40,43,3
4. Research results=43,46,6
Section4. Recommendations for Results and Expected Effects=49,52,1
1. Application field=49,52,1
2. Expectation effect=49,52,3
Section5. Organization of the Report=51,54,2
Chapter2 Study on XML Information Security Technology=53,56,4
Section1. XML Digital Signature=56,59,3
Section2. XML Encryption=59,62,3
Section3. XML Key Management Service=61,64,4
Section4. XML based Access Control Technique=64,67,5
Section5. XML based Security Information Exchange Technique=68,71,5
Chapter3 Trend in XML Information Security Technology=73,76,3
Section1. Trend of Standardization=75,78,11
Section2. Market Trend=85,88,5
Section3. Products=89,92,6
Chapter4. Study on Standardization Plans for applications of XML Information Security=95,98,3
Section1. Study on XML Signature Conformance Test=97,100,2
1. Plan=98,101,6
2. Test suites and devices=103,106,4
3. Further works=107,110,3
Section2. Study on Applying XACML to UDDI Access Control=109,112,2
1. Overview of UDDI=110,113,5
2. Integration of UDDI and XACML=114,117,5
Section3. Study on Security Standardization for E-Government=118,121,1
1. Overview of e-government services=118,121,2
2. Security requirements=119,122,10
Chapter5 Conclusion=129,132,4
Appendix=133,136,2
Appendix A. References=135,138,6
Appendix B. Terminologies and Abbreviations=141,144,2
Appendix C. List of Research Results=143,146,1
1. Summary of Results=143,146,1
2. Standard Developments=143,146,2
3. Patents=145,148,1
4. Papers=145,148,2
5. Softwares=146,149,1
6. TM/TDP=147,150,2
AppendixD. Summary of Standards=149,152,15
[그림2-1] XML 전자서명 구조 및 전자서명 생성 절차=57,60,1
[그림2-2] XML 암호 기술에서 암호화 절차=60,63,1
[그림2-3] XML 암호 기술에서 복호화 절차=61,64,1
[그림2-4] XKMS의 키등록 절차=63,66,1
[그림2-5] XACML 처리 절차 개념도=68,71,1
[그림2-6] SAML 생산자-소비자 모델=70,73,1
[그림2-7] SAML 바인딩과 프로파일=71,74,1
[그림3-1] 웹서비스 보안 기술 관련 표준화 단체=76,79,1
[그림3-2] XML과 웹서비스를 금융 서비스에 도입하기 어려운 이유=89,92,1
[그림3-3] XML Hyper Cycle 2003, Gartner=92,95,1
[그림4-1] 표준 적합성 검사 과정=106,109,1
[그림4-2] UDDI 정보 모델=111,114,1
[그림4-3] UDDI 정보 모델과 WSDL의 매핑=113,116,1
[그림4-4] XACML을 이용한 UDDI 접근제어 구조=115,118,1
[그림4-5] 접근제어 처리과정의 순차 다이어그램=116,119,1
[그림4-6] 각 국가별 전자정부 발전 단계=119,122,1
[그림4-7] 웹서비스 보안 기술 적용 구간=122,125,1
[그림4-8] 대기업 서비스에서의 웹서비스 보안적용 시나리오=124,127,1
*표시는 필수 입력사항입니다.
| 전화번호 |
|---|
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
| 번호 | 발행일자 | 권호명 | 제본정보 | 자료실 | 원문 | 신청 페이지 |
|---|
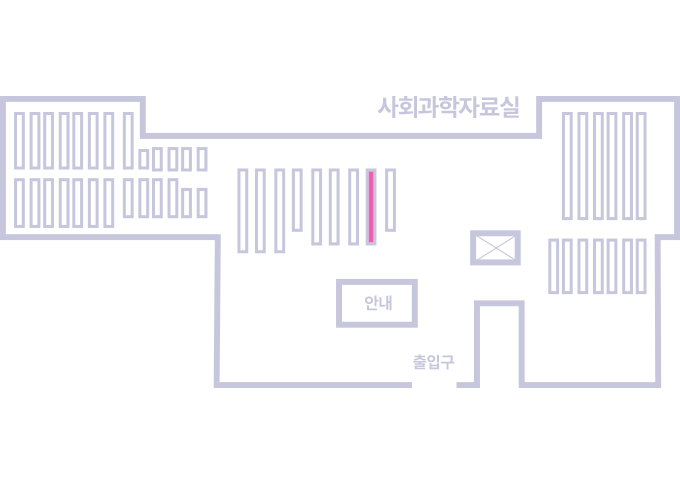
도서위치안내: / 서가번호:
우편복사 목록담기를 완료하였습니다.
*표시는 필수 입력사항입니다.
저장 되었습니다.