대표어
 https://documents.worldbank.org/en/publication/documents-reports/documentdetail/099082726105520284
권호기사보기
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
결과 내 검색
동의어 포함
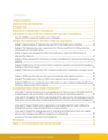
Title page 1
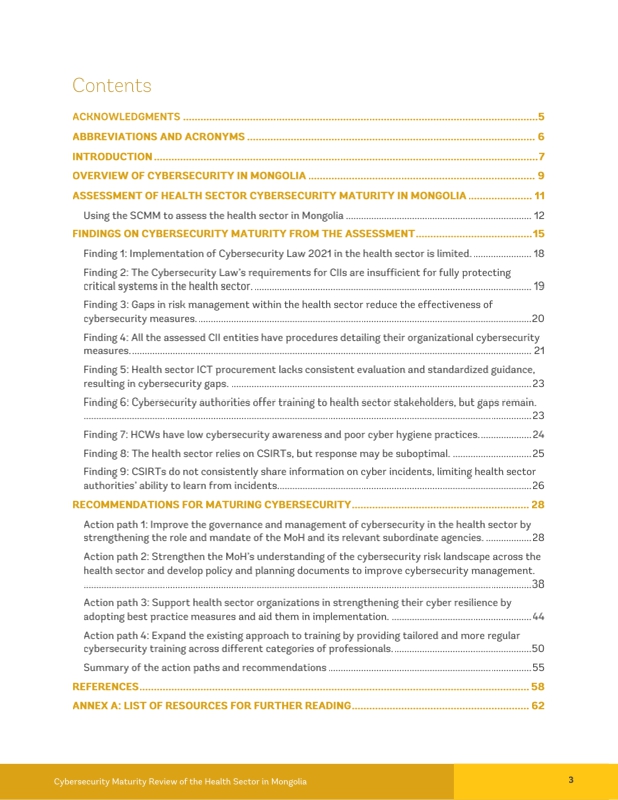
Contents 4
Acknowledgments 6
Abbreviations and Acronyms 7
Introduction 8
Overview of Cybersecurity in Mongolia 10
Assessment of Health Sector Cybersecurity Maturity in Mongolia 12
Using the SCMM to assess the health sector in Mongolia 13
Findings on Cybersecurity Maturity from the Assessment 16
Finding 1: Implementation of Cybersecurity Law 2021 in the health sector is limited 19
Finding 2: The Cybersecurity Law's requirements for CIIs are insufficient for fully protecting critical systems in the health sector 20
Finding 3: Gaps in risk management within the health sector reduce the effectiveness of cybersecurity measures 21
Finding 4: All the assessed CII entities have procedures detailing their organizational cybersecurity measures 22
Finding 5: Health sector ICT procurement lacks consistent evaluation and standardized guidance, resulting in cybersecurity gaps 24
Finding 6: Cybersecurity authorities offer training to health sector stakeholders, but gaps remain 24
Finding 7: HCWs have low cybersecurity awareness and poor cyber hygiene practices 25
Finding 8: The health sector relies on CSIRTs, but response may be suboptimal 26
Finding 9: CSIRTs do not consistently share information on cyber incidents, limiting health sector authorities' ability to learn from incidents 27
Recommendations for Maturing Cybersecurity 29
Action path 1: Improve the governance and management of cybersecurity in the health sector by strengthening the role and mandate... 29
Action path 2: Strengthen the MoH's understanding of the cybersecurity risk landscape across the health sector and develop policy and... 39
Action path 3: Support health sector organizations in strengthening their cyber resilience by adopting best practice measures and aid... 45
Action path 4: Expand the existing approach to training by providing tailored and more regular cybersecurity training across different... 51
Summary of the action paths and recommendations 56
References 59
Annex A. List of resources for further reading 63
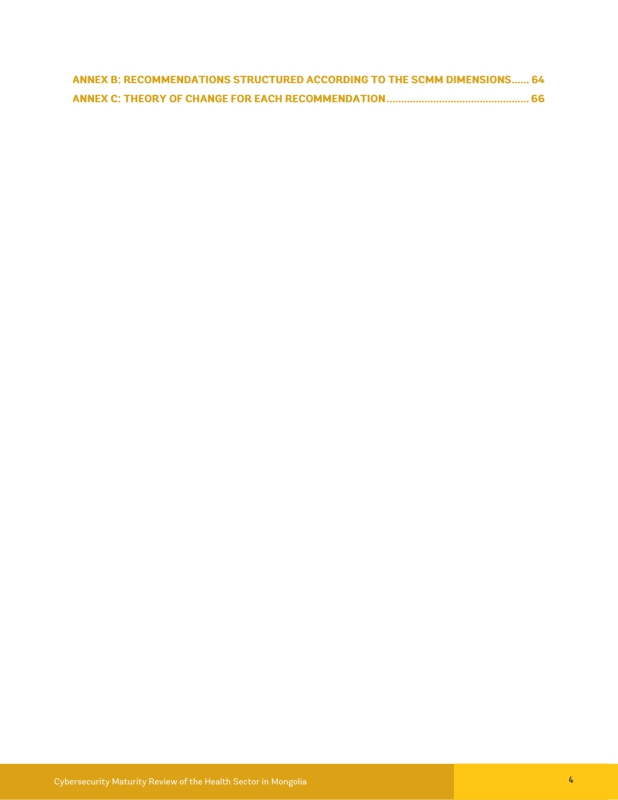
Annex B. Recommendations Structured According to the SCMM Dimensions 65
Annex C. Theory of change for each recommendation 67
Figure 1. National Institute of Standards and Technology Cybersecurity Framework 2.0 19
Figure 2. Lessons from the National Institute of Standards and Technology Cybersecurity Framework 28
Figure 3. The Four Action Paths 29
Figure 4. Theory of Change Related to Implementation of Recommendation 1 30
Figure 5. Theory of Change Related to Implementation of Recommendation 2 35
Figure 6. Theory of Change Related to Implementation of Recommendation 3 36
Figure 7. Theory of Change Related to Implementation of Recommendation 4 38
Figure 8. Theory of Change Related to Implementation of Recommendation 5 40
Figure 9. Theory of Change Related to Implementation of Recommendation 6 41
Figure 10. Inexhaustive List of Cyber Risk Categories 42
Figure 11. Theory of Change Related to Implementation of Recommendation 7 44
Figure 12. National Institute of Standards and Technology Incident Response Life Cycle 45
Figure 13. Theory of Change Related to Implementation of Recommendation 8 46
Figure 14. Theory of Change Related to Implementation of Recommendation 9 52
Boxes 12
Box 1. Maturity Levels 12
Box 2. Measures to Respond to Cyberattacks and Violations, as Mandated in the Common Procedure 27
Box 3. Approaches to Managing Health Sector Emergency and Incident Response: A Health Sector-Specific Computer Emergency... 32
Box 4. Connecting Recommendation 1 to the Assessment Findings 34
Box 5. Connecting Recommendation 2 to the Assessment Findings 36
Box 6. Connecting Recommendation 3 to the Assessment Findings 37
Box 7. Connecting Recommendation 4 to the Assessment Findings 39
Box 8. Connecting Recommendation 5 to the Assessment Findings 40
Box 9. Connecting Recommendation 6 to the Assessment Findings 43
Box 10. Connecting Recommendation 7 to the Assessment Findings 45
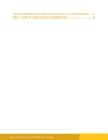
Box 11. Development of Minimum Cybersecurity Standards Designed to Assist Organizations in Managing Security Risks and Their Impact... 47
Box 12. Connecting Recommendation 8 to the Assessment Findings 51
Box 13. Approach to Building Cybersecurity Awareness and Skills among Health Care Providers in Estonia 54
Box 14. Connecting Recommendation 9 to the Assessment Findings 56
*표시는 필수 입력사항입니다.
| 전화번호 |
|---|
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
| 번호 | 발행일자 | 권호명 | 제본정보 | 자료실 | 원문 | 신청 페이지 |
|---|
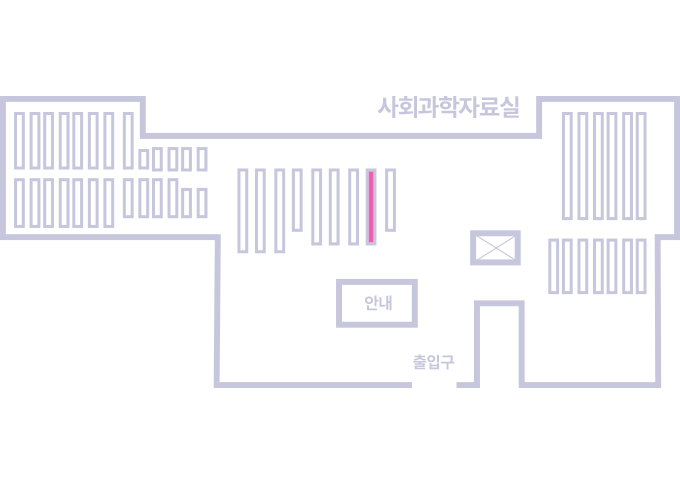
도서위치안내: / 서가번호:
우편복사 목록담기를 완료하였습니다.
*표시는 필수 입력사항입니다.
저장 되었습니다.