대표어
 https://csrc.nist.gov/pubs/sp/800/213/a/r1/iprd
권호기사보기
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
결과 내 검색
동의어 포함
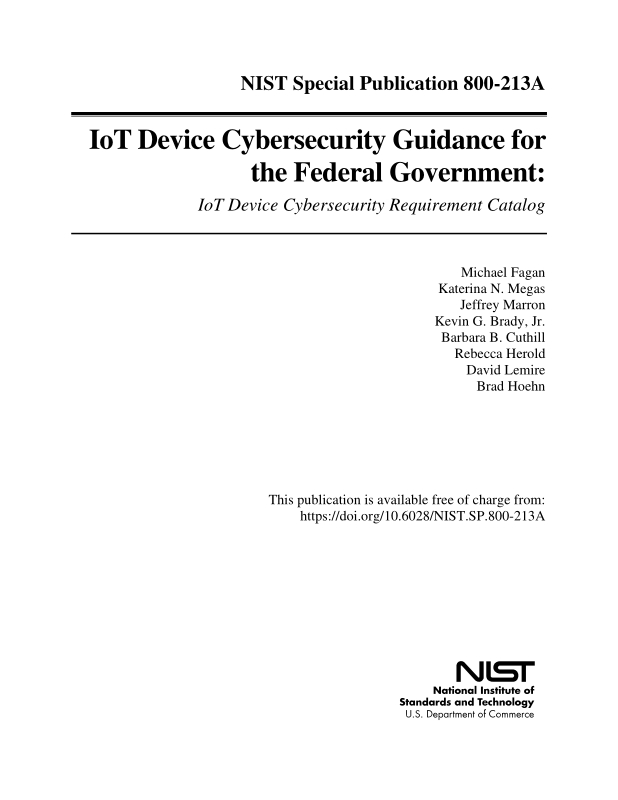
Title page 1
Contents 7
Abstract 4
Acknowledgments 5
1. Introduction 10
1.1. Purpose and Applicability 10
1.2. Target Audience 11
1.3. Relationship to Other Publications 11
1.4. Publication Organization 11
2. Device Cybersecurity Capability Catalog 14
DI - DEVICE IDENTIFICATION 15
(IMS) Identifier Management Support 15
(AID) Actions Based on Device Identity 15
(DAS) Device Authentication Support 16
(PID) Physical Identifiers 16
DC - DEVICE CONFIGURATION 17
(PRV) Logical Access Privilege Configuration 17
(AUT) Authentication and Authorization Configuration 17
(INT) Interface Configuration 17
(DSP) Display Configuration 18
(CTL) Device Configuration Control 18
DP - DATA PROTECTION 19
(CRY) Cryptography Capabilities and Support 19
(KEY) Cryptographic Key Management 19
(STO) Secure Storage 20
(STX) Secure Transmission 20
LA - LOGICAL ACCESS TO INTERFACES 22
(AUN) Authentication Support 22
(ACF) Authentication Configuration 23
(USE) System Use Notification Support 23
(AUZ) Authorization Support 24
(AIM) Authentication & Identity Management 24
(ROL) Role Support & Management 24
(LDU) Limitations on Device Usage 26
(XCN) External Connections 27
(IFC) Interface Control 27
SU - SOFTWARE UPDATE 29
(UPD) Update Capabilities 29
(APP) Update Application Support 30
CS - CYBERSECURITY STATE AWARENESS 31
(AEI) Access to Event Information 31
(EIM) Event Identification & Monitoring 31
(EVR) Event Response 32
(LCT) Logging Capture & Trigger Support 33
(RDL) Support of Required Data Logging 33
(LSR) Audit Log Storage & Retention 34
(SRT) Support for Reliable Time 34
(AUP) Audit Support & Protection 35
(AWR) State Awareness Support 36
DS - DEVICE SECURITY 37
(EXE) Secure Execution 37
(COM) Secure Communication 37
(RSC) Secure Resource Usage 38
(DIN) Device Integrity 39
(ONB) Secure Network Onboarding Support 39
(OPS) Secure Device Operation 40
3. Non-Technical Supporting Capability Catalog 42
DO - DOCUMENTATION 43
(SMP) Assumptions Made in Product Development 43
(CAP) Technical Cybersecurity Capabilities Implemented 50
(DSC) Design and Support Considerations 52
(MNT) Maintenance Requirements 54
(DAU) Device Authenticity Support 56
IQ - INFORMATION AND QUERY RECEPTION 57
(BUG) Reception of Vulnerability Information 57
(QRY) Query Response 58
ID - INFORMATION DISSEMINATION 60
(CRI) Cybersecurity Related Information Alert 60
(VNT) Cybersecurity Event Notification 62
EA - EDUCATION AND AWARENESS 64
(CSC) Cybersecurity Capabilities 64
(EOL) End-of-Life (Reprovisioning and Disposal) 66
(RSP) Cybersecurity Responsibilities 66
(EXP) Cybersecurity Expectations and Assumptions 67
(BAK) Data Back-up 68
(VMG) Vulnerability Management Options 69
References 71
Appendix A. Definition of the Federal Profile for IoT Device Cybersecurity Requirements 73
Appendix B. Mapping of SP 800-53 Controls to Device Cybersecurity Requirements 77
Appendix C. Mapping of Cybersecurity Framework Outcomes to Device Cybersecurity Requirements 85
Appendix D. Acronyms 93
Appendix E. Glossary 94
Figure 1. Capability and Sub-Capability Structure 12
*표시는 필수 입력사항입니다.
| 전화번호 |
|---|
| 기사명 | 저자명 | 페이지 | 원문 | 기사목차 |
|---|
| 번호 | 발행일자 | 권호명 | 제본정보 | 자료실 | 원문 | 신청 페이지 |
|---|
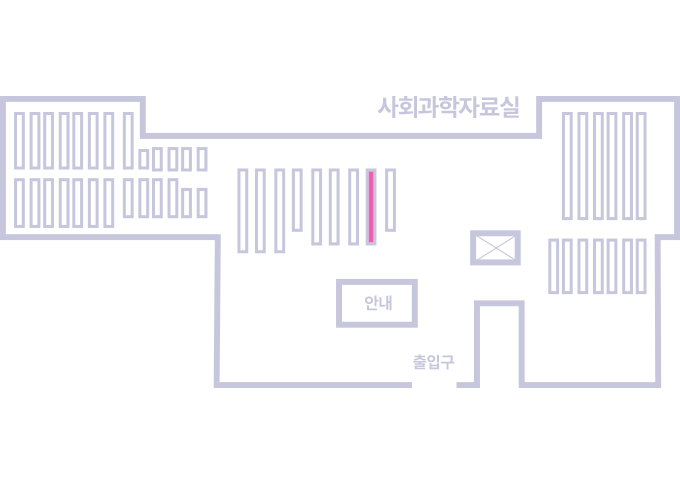
도서위치안내: / 서가번호:
우편복사 목록담기를 완료하였습니다.
*표시는 필수 입력사항입니다.
저장 되었습니다.